This note explains the standard MailsDrop temporary inbox as it is designed in September 2026. It is an implementation and product-scope note, not a promise of anonymity, a legal opinion, or a claim that every temporary-email provider works the same way. The goal is to make one practical boundary clear: a standard MailsDrop inbox is intended for short-lived, low-risk message receipt during an active session, not for long-term message storage or account recovery.
Short answer: MailsDrop creates a temporary address for a standard inbox, receives an inbound message for a supported domain, prepares a safe display payload, and sends it to the active inbox session in real time. Standard temporary messages are not treated as a permanent mailbox archive. A separate premium mailbox product has different storage behaviour and is outside the scope of this note.
Why publish a technical note?
Temporary email is often described with broad labels such as “private,” “instant,” or “disposable.” Those labels can be useful, but they do not explain what happens to a message, what a browser session means, or when a user should choose a normal mailbox instead. This note documents the intended standard-inbox lifecycle so readers can make a better decision before sending a verification message or using a generated address.
It also draws a firm line around what MailsDrop does not claim. A temporary address does not make a person anonymous. It does not replace a password manager, multi-factor authentication, or a persistent recovery inbox. It should not receive passwords, recovery codes, payment information, identity documents, private files, health information, or work-related secrets.
Scope: standard temporary inboxes only
This article covers the standard temporary inbox available without registration. It does not describe premium custom mailboxes, which are a separate product path with their own account and message-storage features. Treating the two as identical would be misleading: a standard temporary inbox is deliberately short lived, while a premium mailbox is designed for an authenticated user who needs durable account-level features.
| Feature | Standard temporary inbox | Premium mailbox |
|---|---|---|
| Intended use | Brief, low-risk receipt during an active session. | Authenticated, longer-term mailbox use. |
| Message handling | Delivered to the current session rather than offered as a permanent archive. | Uses a separate product path with stored message features. |
| Account recovery | Not appropriate. | Still depends on the user's account and applicable product settings. |
| Suitable for sensitive information | No. | Use only according to the product's terms and your own security requirements. |
If you need a broader introduction before this technical note, start with what temporary email is and when to use it.
The standard temporary-inbox delivery path
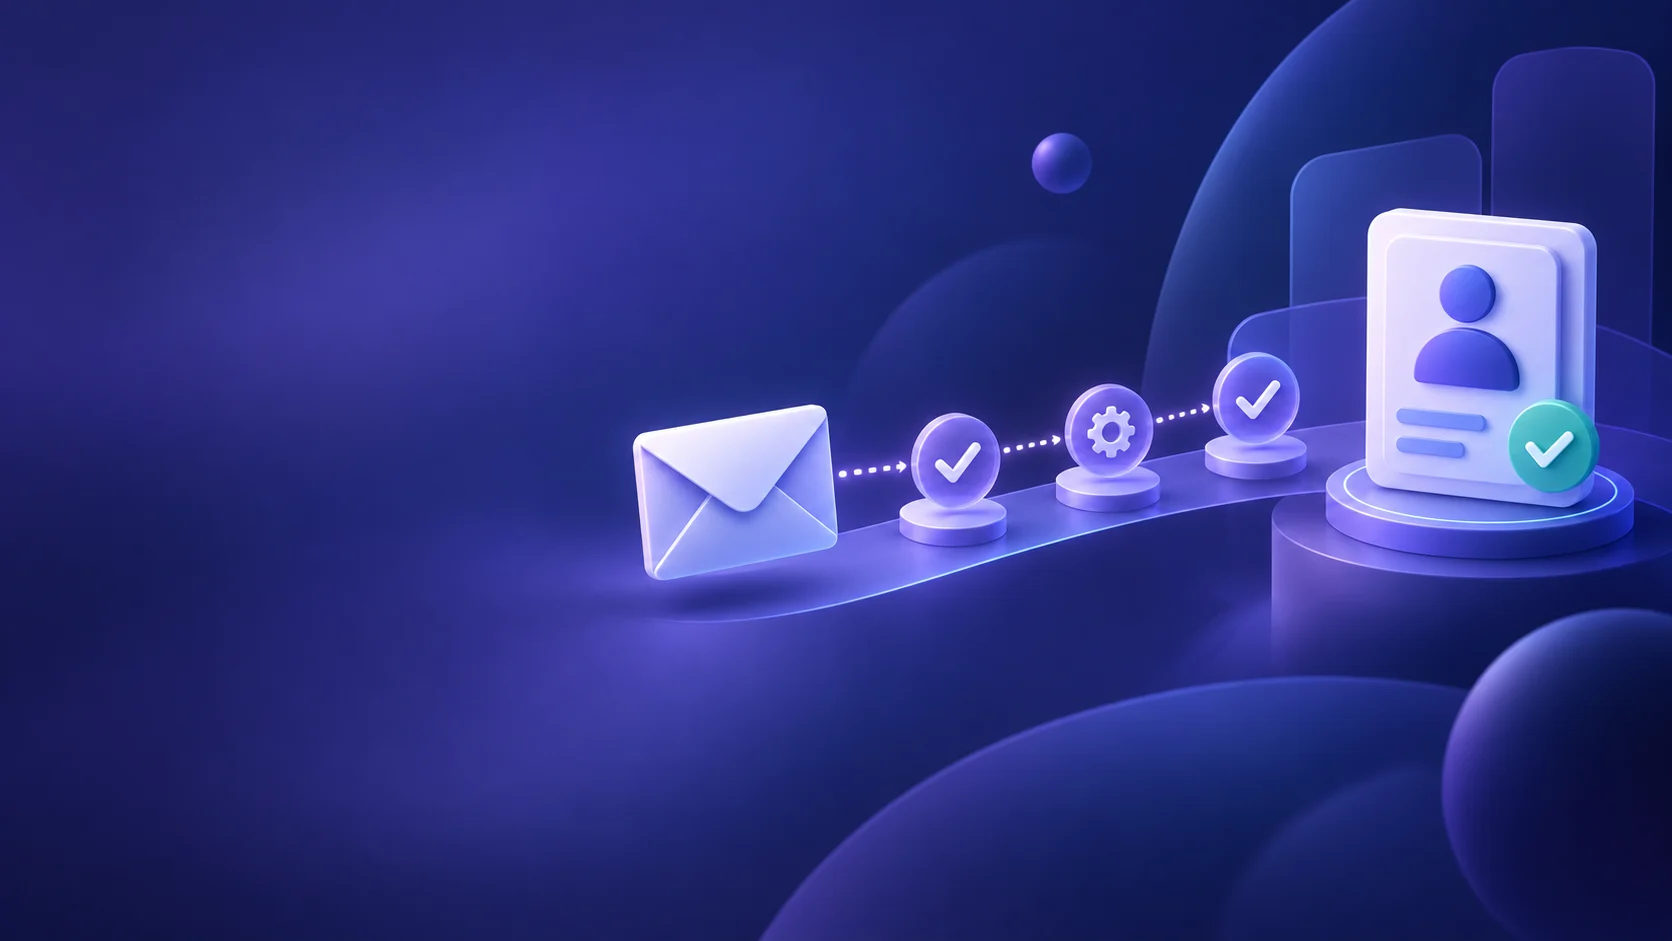
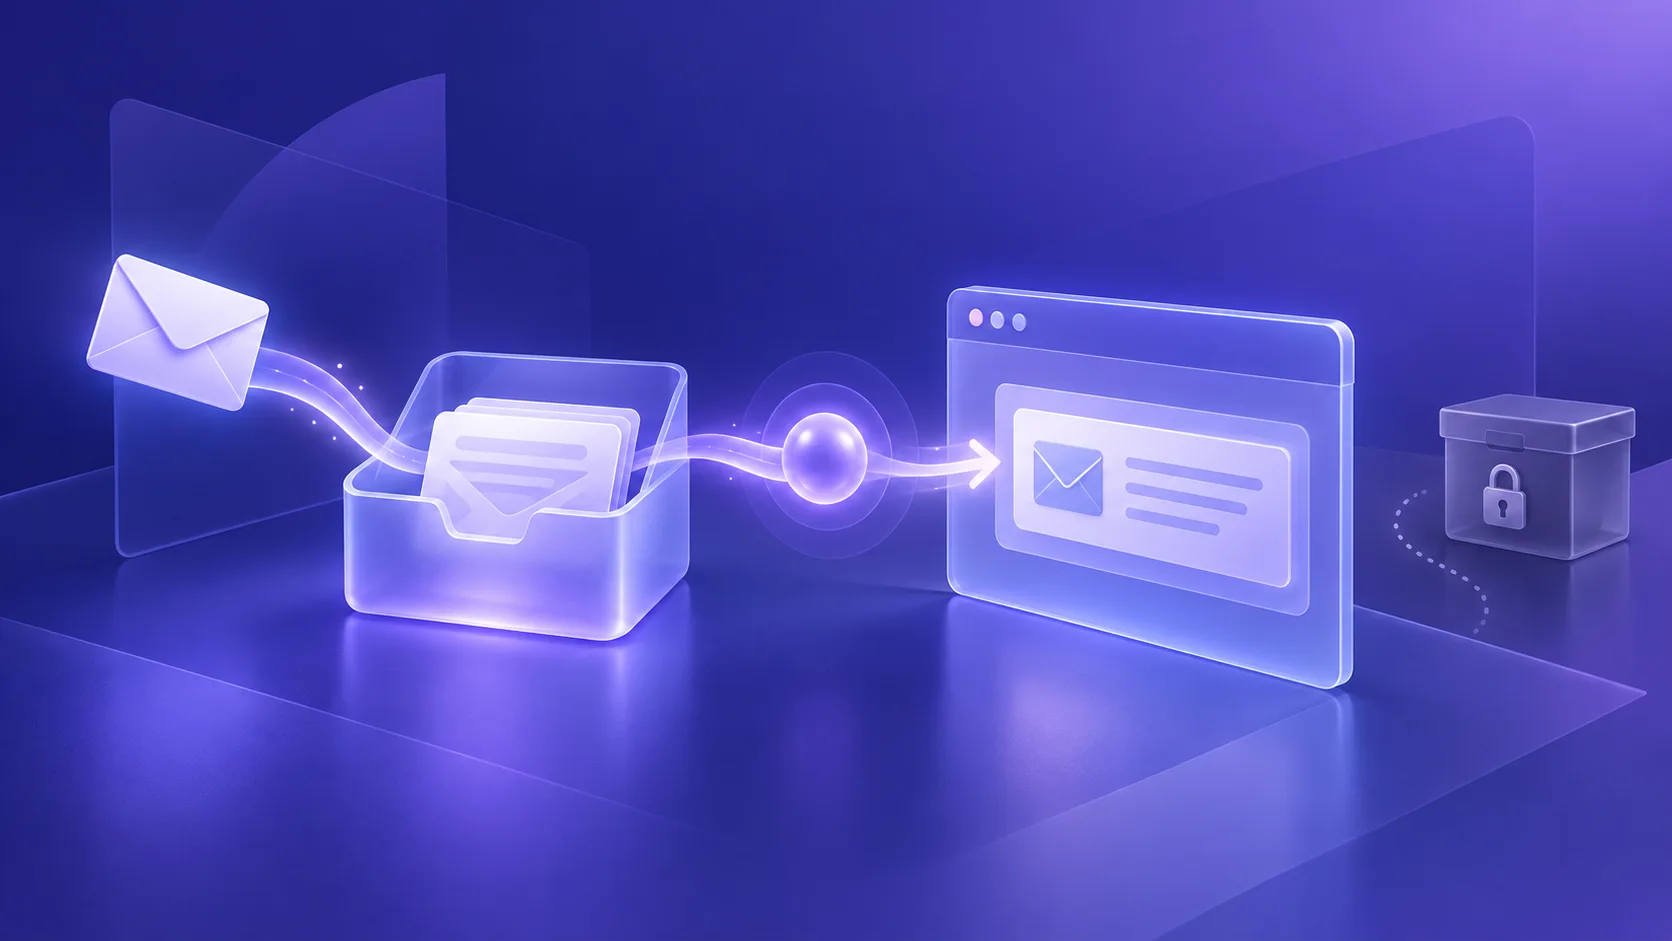
The standard flow has five practical stages. The details below are intentionally high level: they explain the product boundary without disclosing service secrets or providing a map for bypassing protections.
- An address is generated. When a visitor opens the temporary inbox tool, MailsDrop creates a random address under a supported temporary domain and associates it with a session-specific access identifier.
- A sender addresses a message to that inbox. The sending system routes the message to the supported MailsDrop domain. Standard email delivery can be delayed or rejected by the sender or an intermediary, so a generated address is not a promise that every website will accept it.
- MailsDrop recognizes the recipient domain. The inbound path checks that the message is addressed to a domain operated by MailsDrop before it is considered for delivery to a temporary inbox.
- A display-safe payload is prepared. The inbound message data is handled for browser display; HTML content is sanitized before it is sent to the client-facing delivery path.
- The message is delivered to the active session in real time. The standard path broadcasts the message to the session associated with the generated inbox, allowing the browser to show it without treating the inbox as a long-term archive.
“Real time” describes the user experience after MailsDrop receives and processes a message. It does not guarantee that a sender will send immediately, that every outside service will accept a temporary address, or that every network will deliver without delay. Those are separate parts of the email ecosystem.
What session-based access means in practice
A session is the active context that lets a browser display a specific temporary inbox. It is useful for a short task: you can keep the inbox open while waiting for an expected verification message, check the sender and message context, and complete the permitted action. It is not a substitute for owning a durable mailbox.
As documented in the MailsDrop Privacy Policy, the standard service is designed around in-memory handling rather than persistent email storage. Browser state, session availability, device changes, clearing browser data, or ending a session can all affect whether a message is still available to you. Do not plan a workflow that needs to retrieve the message later.
For the user-facing consequences of that design, read how long temporary emails last. That guide distinguishes address lifetime, session access, and message retention—three ideas that are often mistakenly treated as one timer.
What the standard inbox does not store as a mailbox archive
The standard temporary-inbox path is not designed to create a permanent user mailbox or a historical message library. A message that is useful for a short confirmation should not be treated as an account record, receipt archive, password-recovery channel, or document store. MailsDrop cannot make a closed or ended standard inbox into a reliable recovery destination.
This statement does not mean that a web service processes no technical information at all. The Privacy Policy describes limited technical data used for operation and anti-abuse purposes, including temporary session-related handling. The right conclusion is not “nothing can ever be processed”; it is that the standard inbox should be used only where short-lived access is appropriate.
Why HTML is handled carefully
Email HTML can contain layouts, images, links, and content that was authored outside MailsDrop. Before a message is sent through the standard browser-delivery path, the application sanitizes HTML intended for display. This reduces the chance that unsafe markup is directly presented as trusted page content.
Sanitizing display content is not a reason to trust every email. A well-formed message can still contain a misleading link, impersonated sender name, or an unexpected request. Check that the sender and subject match the task you just performed, and open important services through a known address or app instead of following a surprising email link. The U.S. Cybersecurity and Infrastructure Security Agency's phishing guidance provides general advice for handling suspicious messages.
What this design is useful for
A standard temporary inbox can be a sensible fit for a legitimate, low-risk, short-lived task. Typical examples include an optional newsletter confirmation, a non-critical download, a product-demo evaluation, or an authorised test of an email form. The benefit is address separation: the destination website receives a temporary address instead of the primary inbox you use every day.
It is not appropriate for banking, payments, healthcare, education, work, travel, government services, legal matters, private documents, subscriptions you plan to keep, or any account that might require a password reset. If losing message access would cause a problem, begin with an inbox you control long term.
A small, responsible verification workflow
- Open the temporary inbox before you start the low-risk task.
- Copy the displayed address carefully into the permitted signup form.
- Keep the inbox session open while you wait for the expected message.
- Confirm the sender, subject, and purpose before using a link or code.
- Complete the immediate task, then do not depend on the inbox for future access.
If a verification email does not arrive, first confirm the exact address you entered, wait briefly, and use the sender's approved resend option if available. Do not create duplicate accounts or try to circumvent a service that rejects temporary addresses. See why verification emails may not arrive for a fuller troubleshooting path.
Limitations and changes
This note describes the intended standard-inbox design as of September 2026. Email delivery depends on sender systems, DNS, network conditions, spam filtering, and policies outside MailsDrop. Product implementation and policy can change as the service evolves. When a statement in this note needs correction, the MailsDrop Team will update the page and preserve its visible update date.
For how we review factual claims and document limitations, see the MailsDrop Methodology. To report a problem without sharing message contents or one-time codes, use the contact page.
Frequently asked questions
Does MailsDrop store standard temporary inbox messages forever?
No. The standard temporary inbox is not offered as a permanent message archive. Use a mailbox you control long term for records, receipts, recovery, or important documents.
Can I reopen the same temporary inbox later?
Do not rely on that. Standard inbox access is session based, and availability can be affected by browser state or the end of the session. Use a permanent mailbox if later access matters.
Does a temporary address make my activity anonymous?
No. It separates your primary email address from a specific signup; it does not erase other information a website processes. Read the privacy limits of temporary email for more context.
Why did a message not appear instantly?
Real-time display begins after MailsDrop receives and processes a message. The sender may delay sending, an outside provider may filter it, or the sender may not accept a temporary address. Keep the session open and follow the sender's approved support or resend flow.
Sources and implementation references
- MailsDrop Privacy Policy — standard temporary-inbox data-handling and session statements.
- MailsDrop Terms of Use — intended temporary-inbox use and recovery limitations.
- MailsDrop Methodology — editorial approach, test boundaries, and correction process.
- CISA: Recognize and Report Phishing — handling unexpected email links and requests safely.